Offensive Security & Pentest
Recon, enumeration and exploitation — web flaws per OWASP Top 10, internal services and privilege escalation, from first scan to root.
GobusterSQLi / XSS
I hunt vulnerabilities before attackers do — offensive testing, Active Directory, cloud hardening and SOC monitoring, documented like a real engagement.
Cybersecurity student on the Cyber Security track at OFPPT's CMC Rabat-Salé-Kénitra, focused on security engineering — cloud security, offensive security and security operations.
Every project on this page is a real lab I built and broke on purpose: Active Directory domains, pfSense and FortiGate firewalls, a Cowrie honeypot, multi-cloud Azure and AWS. Findings land in structured reports with CVSS scoring, PoC evidence and remediation.
Hands-on across offensive and defensive security — built through labs, coursework and a red-board internship cycle.
Recon, enumeration and exploitation — web flaws per OWASP Top 10, internal services and privilege escalation, from first scan to root.

GobusterSQLi / XSS
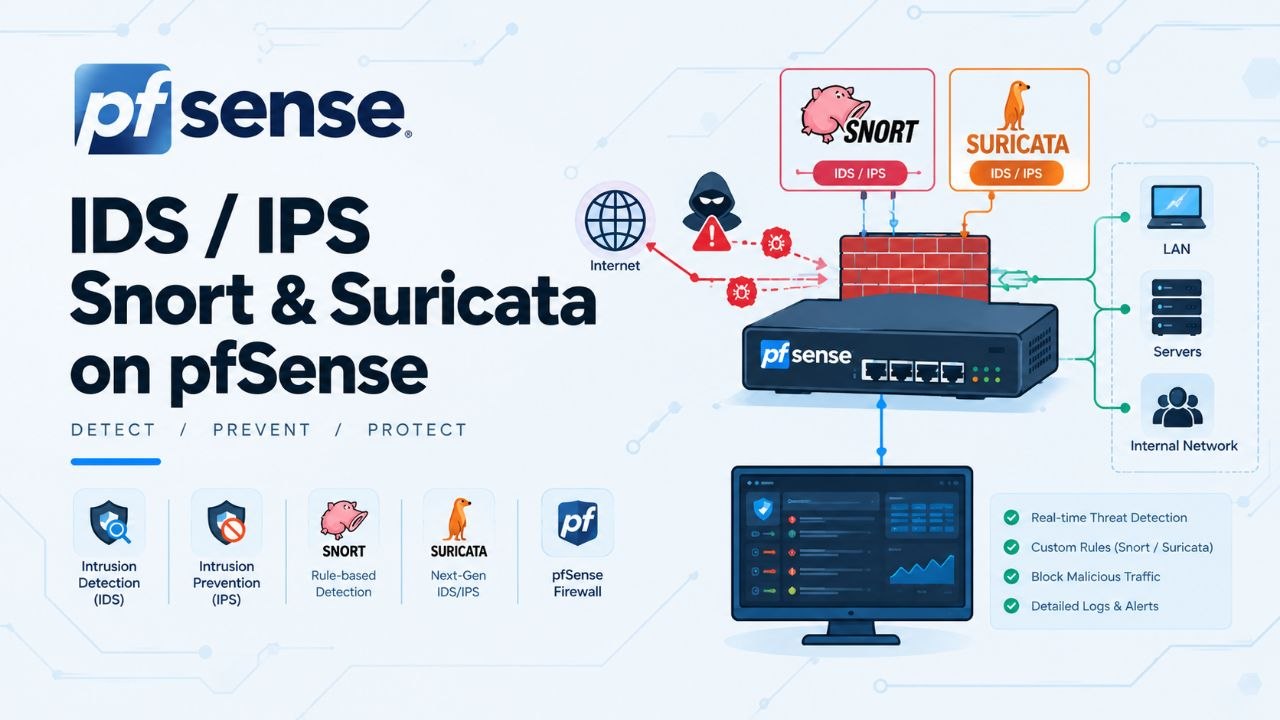
Monitoring, log analysis and incident hunting — SIEM pipelines, ATT&CK mapping, and deep packet analysis when it matters.


Hardening networks, servers and identities — on-prem Active Directory labs plus multi-cloud IAM and segmentation.
Ran reconnaissance and enumeration with Nmap, then exploited OWASP Top 10 weaknesses — SQLi, XSS, SSRF and CSRF — across DVWA and Juice Shop.
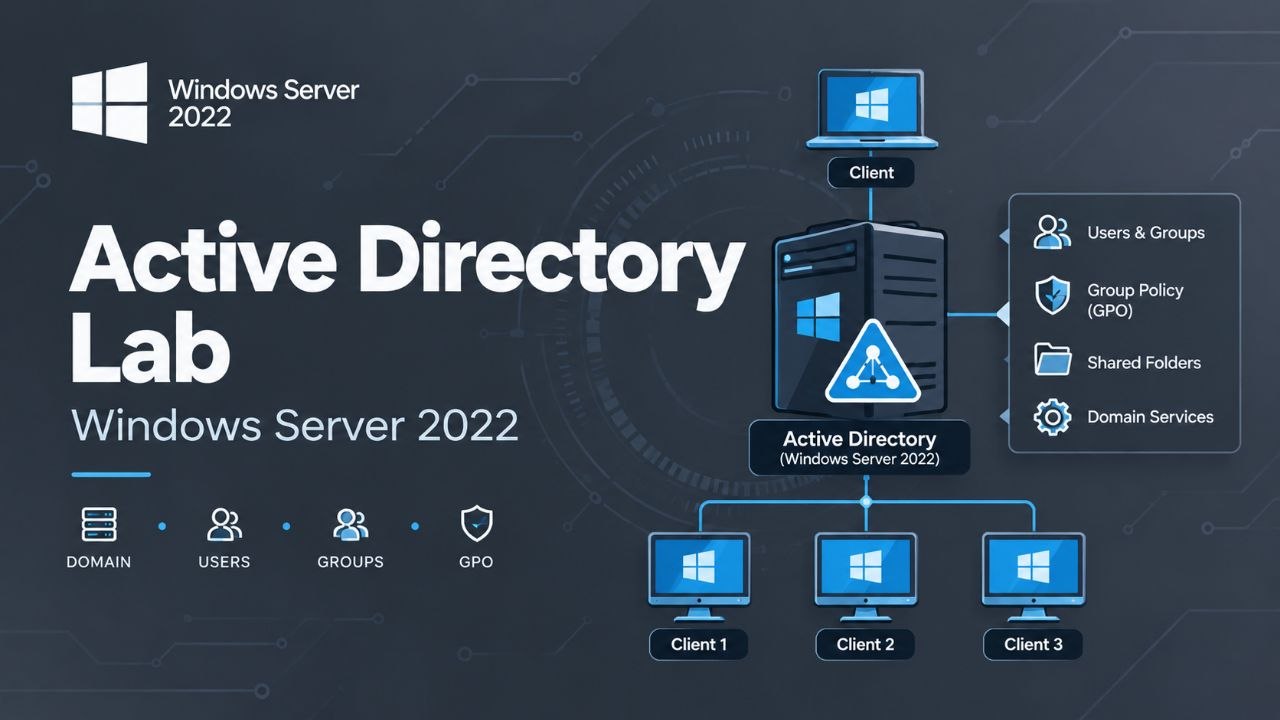
Deployed Active Directory (AD DS, DNS, DHCP) and hardened workstations through Group Policy, then integrated Wazuh and Splunk for centralized log collection.
Built a multi-cloud security lab — Azure VNet, NSG, RBAC and Entra ID alongside AWS IAM users, groups and roles — with positive and negative permission testing on both platforms.
Monitored and analyzed events with Wazuh SIEM, mined Windows Event Logs and Sysmon for IOCs, mapped adversary tactics to MITRE ATT&CK, and simulated attacks with Caldera while dissecting traffic in Wireshark.
Practical work spanning penetration testing, Active Directory and cloud security, and SOC monitoring — every project documented like a real engagement.
Machine learning — Flask
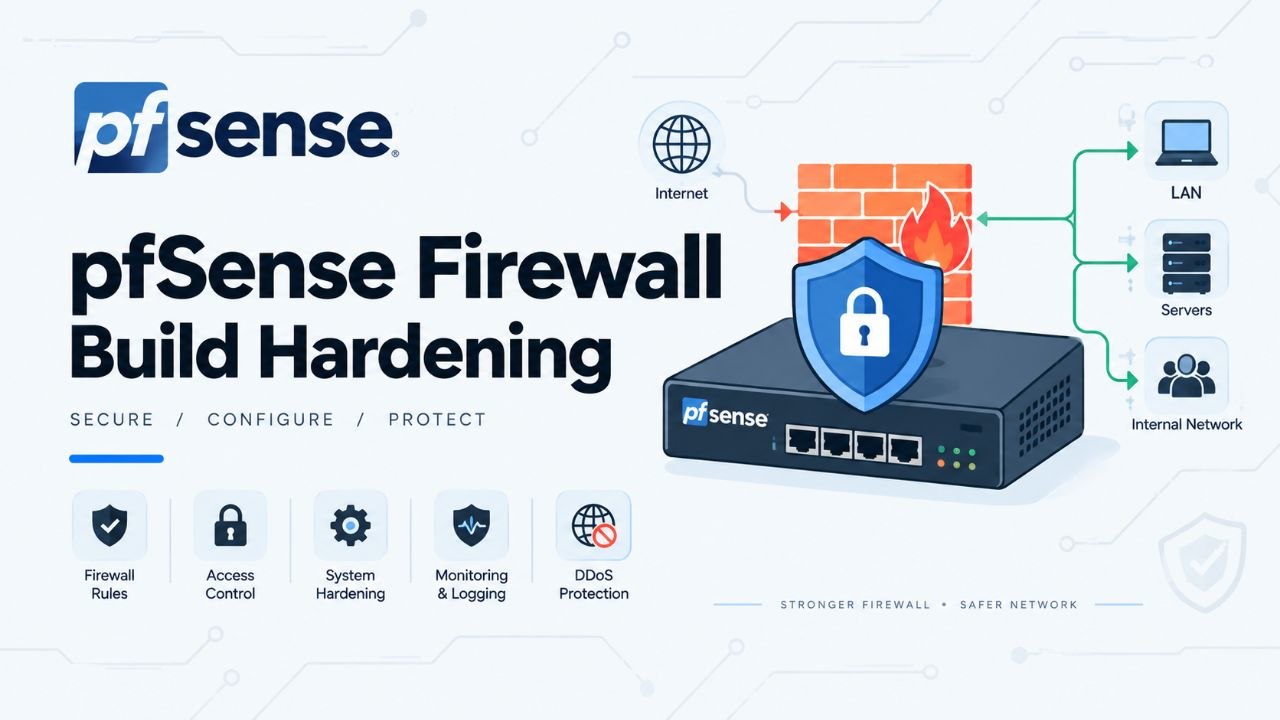
Firewall — Systems hardening
Frontend — HTML, CSS, JS
Network monitoring
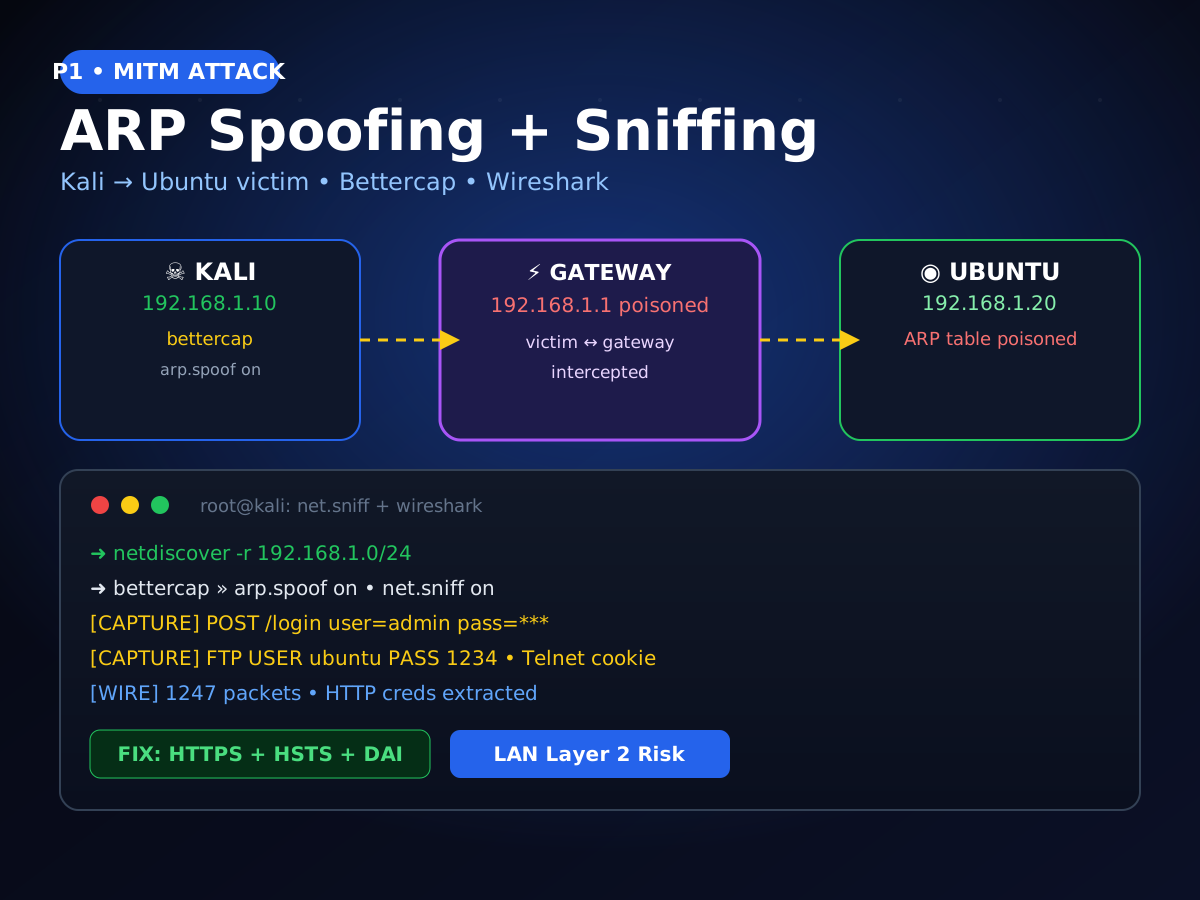
Network — Bettercap, Wireshark
AD DS, DNS, DHCP — VirtualBox
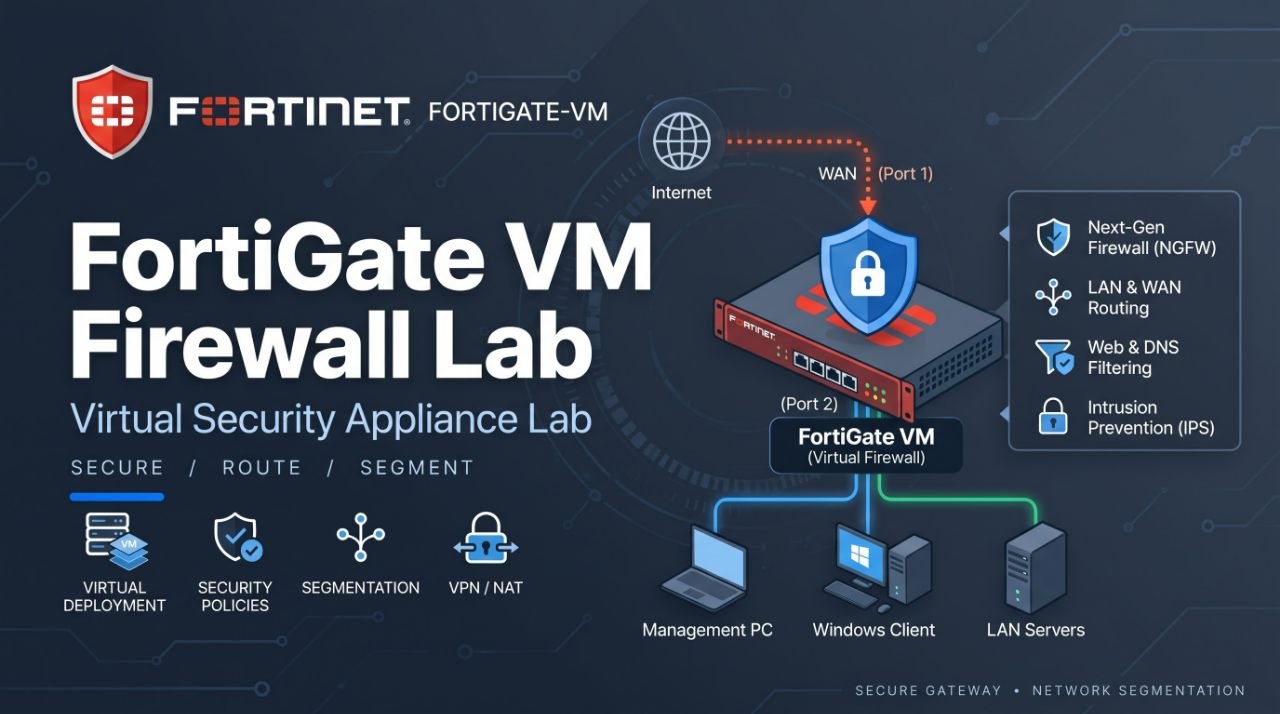
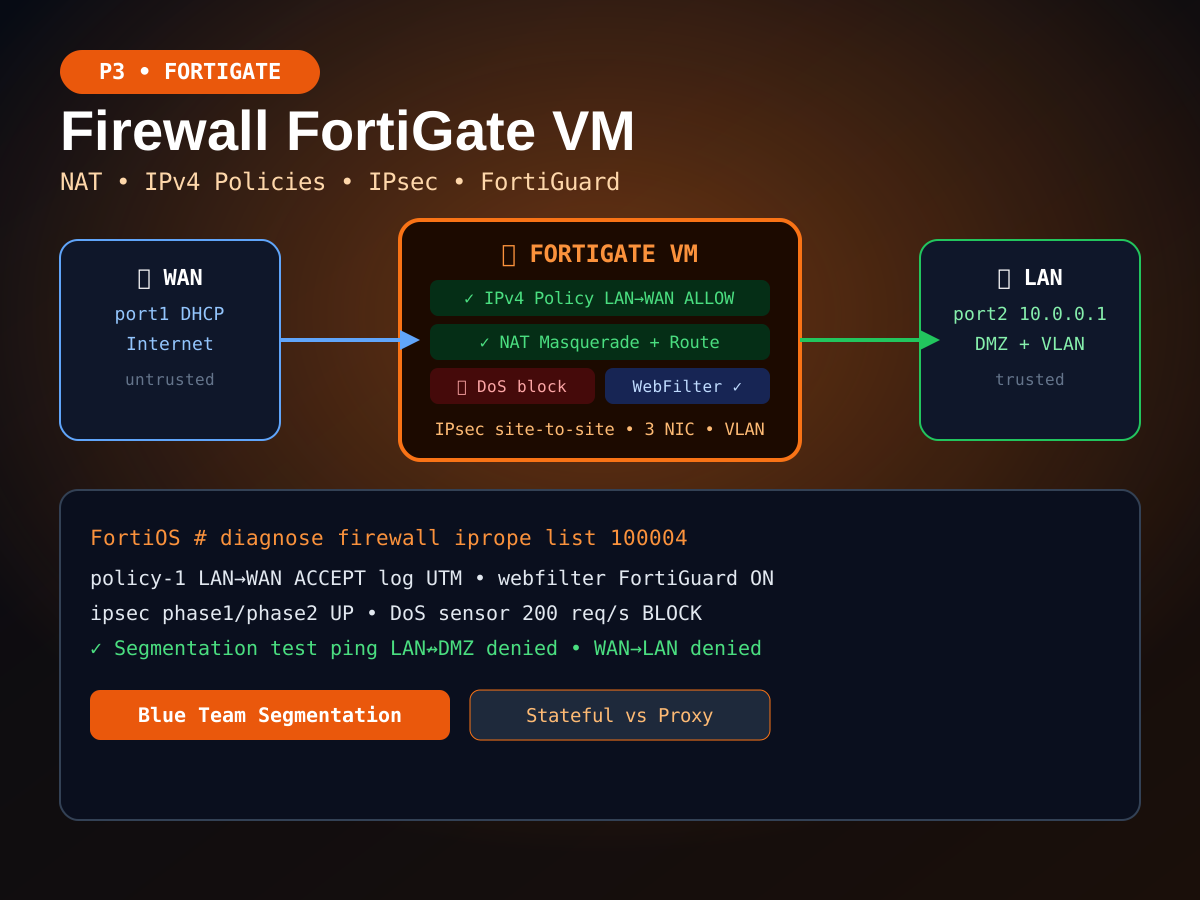
FortiGate VM — NAT, IPsec, web filter
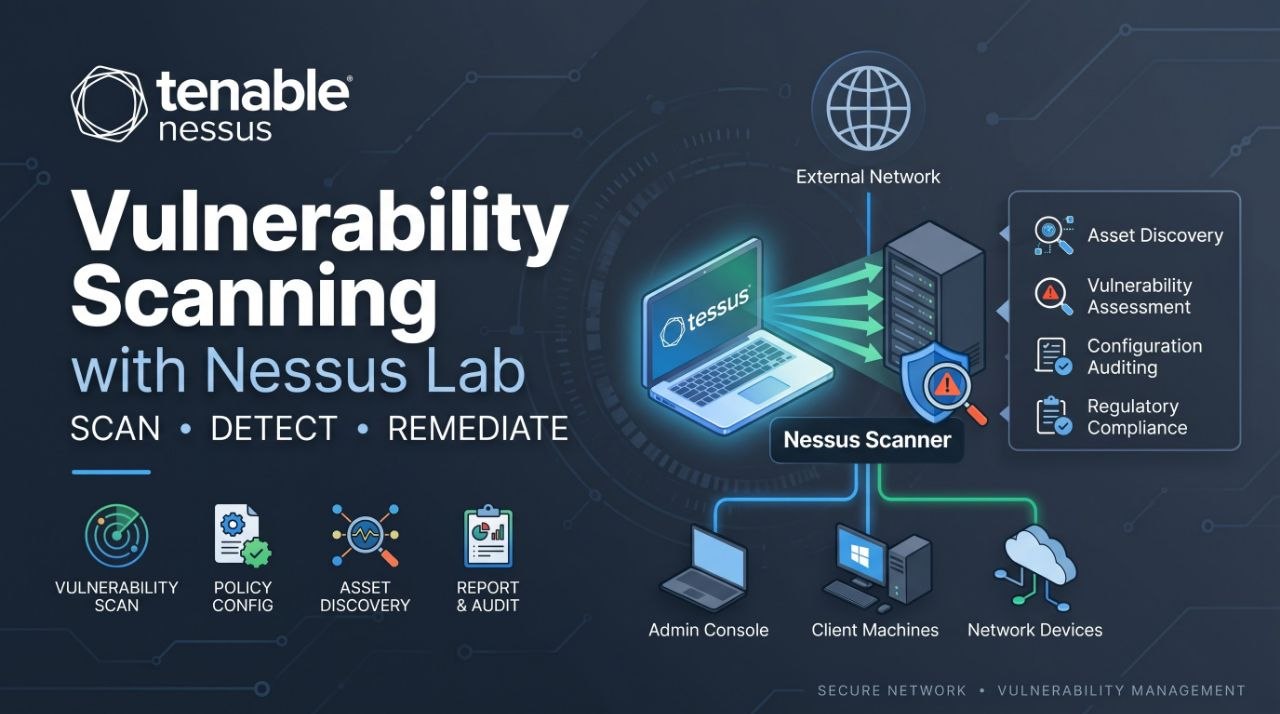
VA — CVE, CVSS, prioritization
Deception — Hydra, Apache, blue team
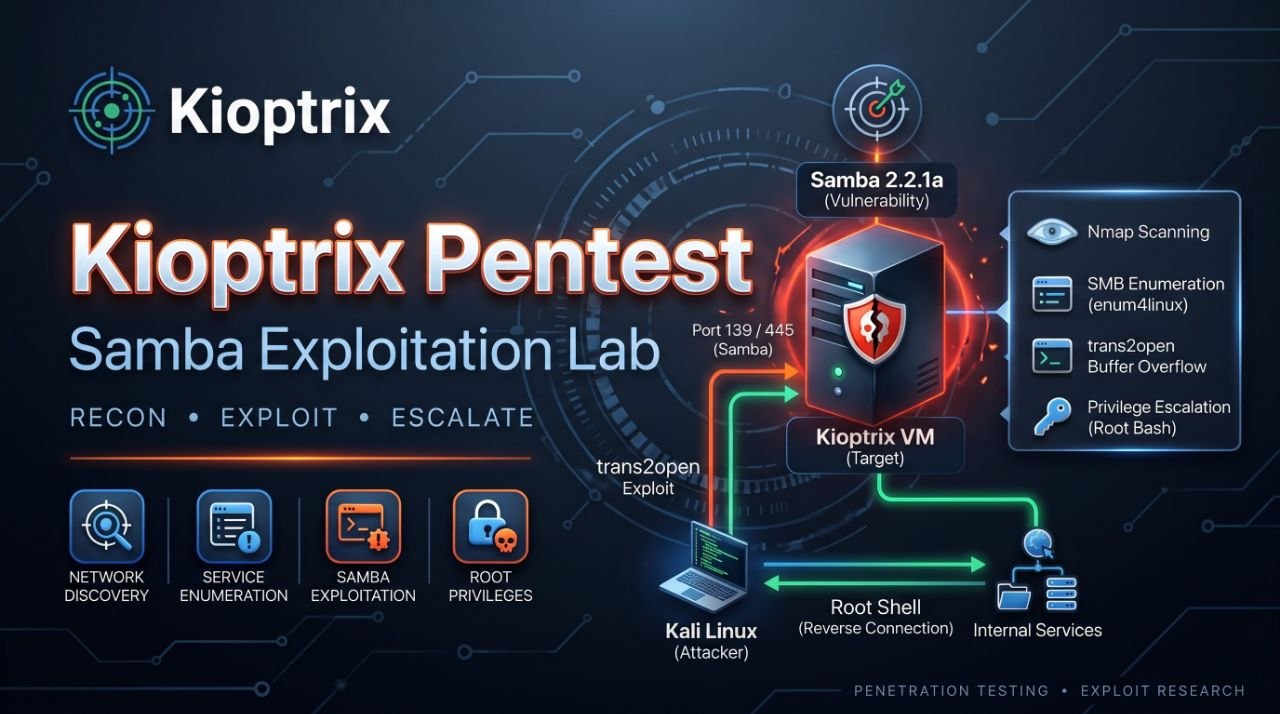
Nmap, Samba 2.2.1a, Metasploit — PTES
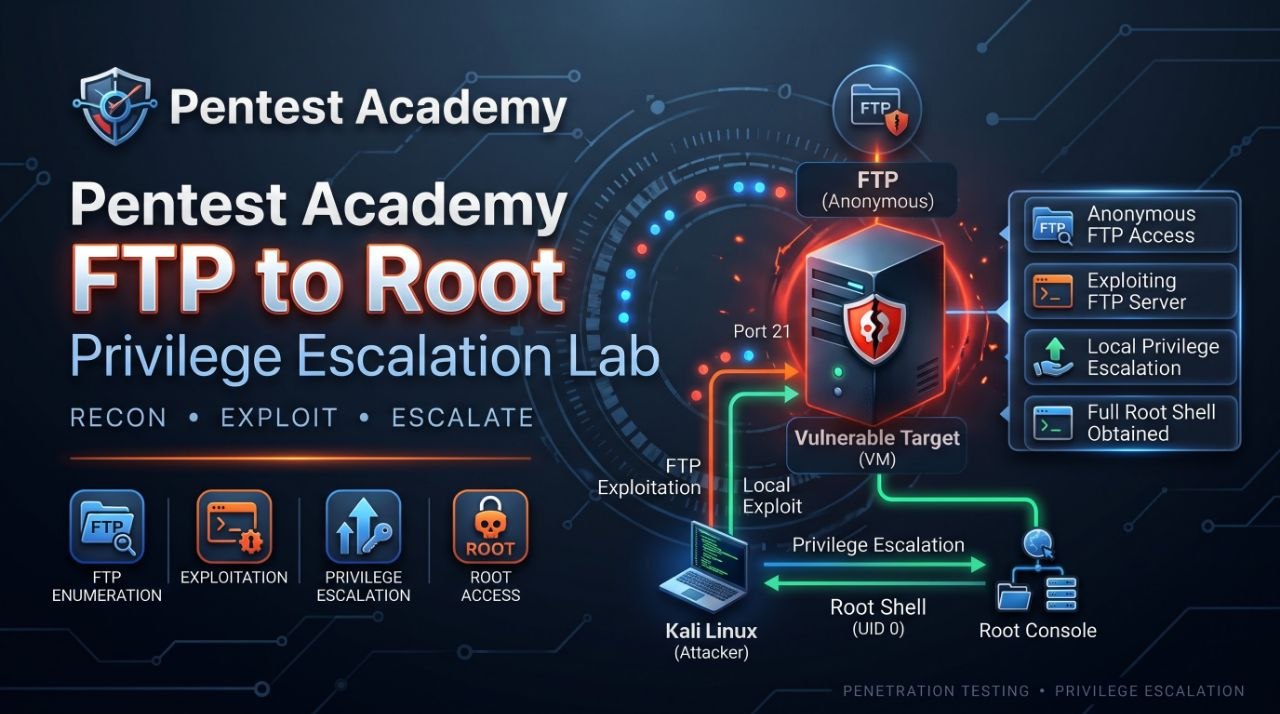
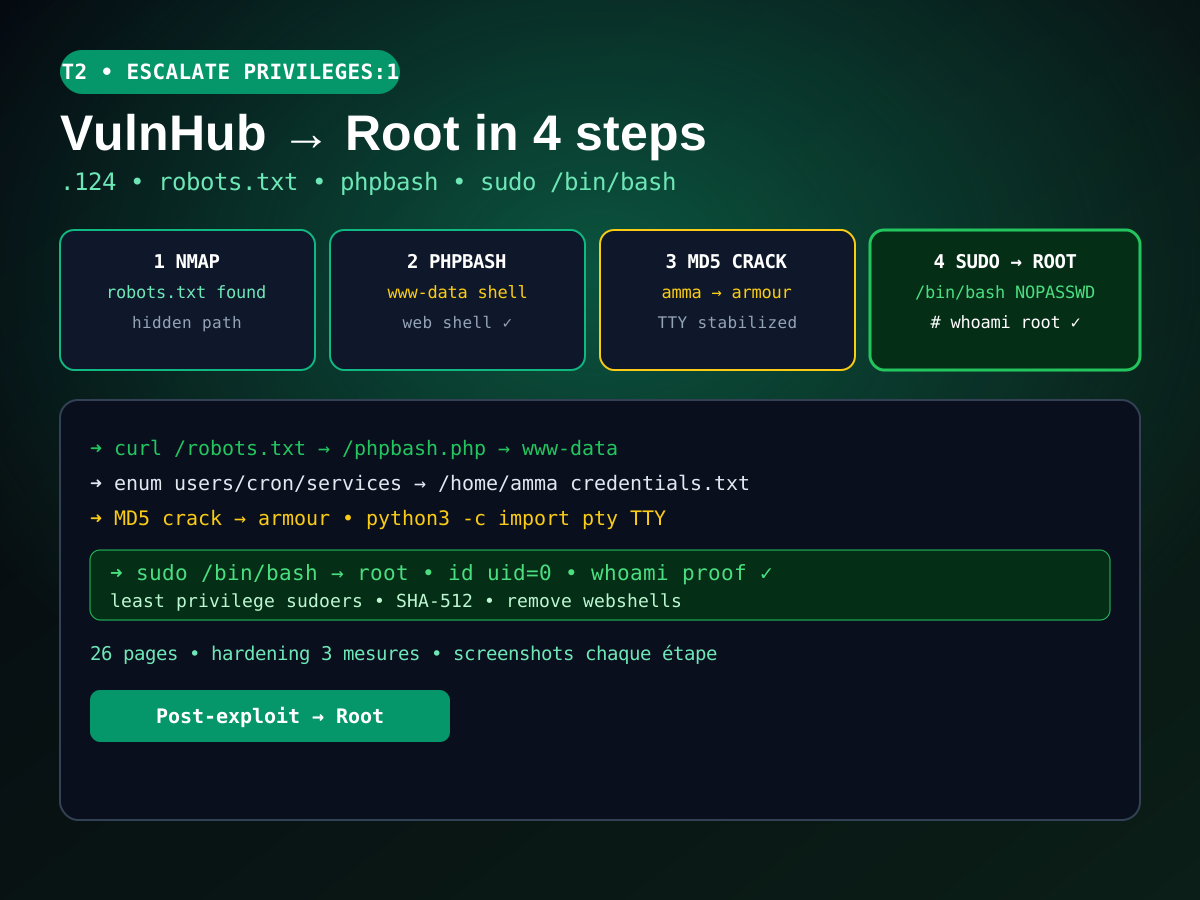
vsftpd, hashcat, LinPEAS — cron privesc
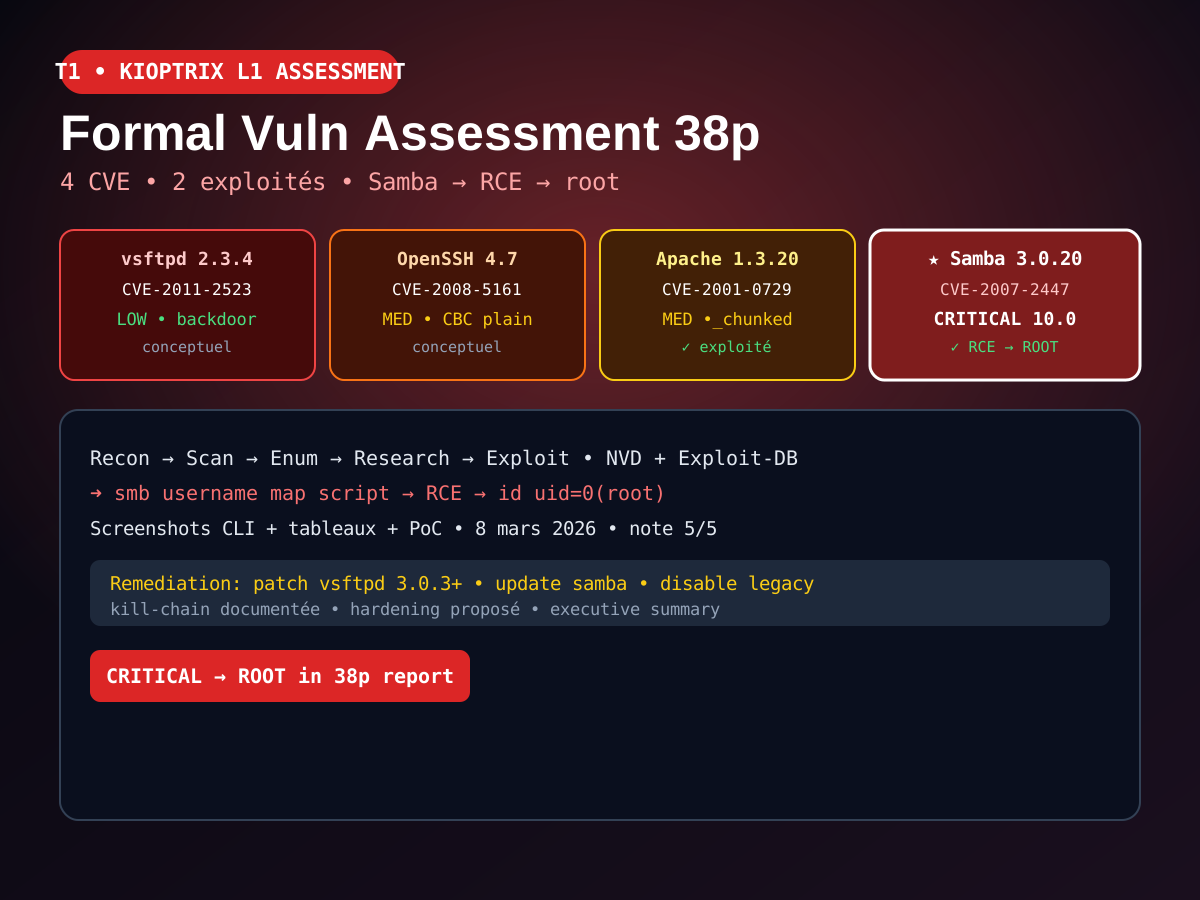
4 CVEs — Samba RCE, CVSS, remediation
VulnHub — web shell, sudo, hardening
SQLi 9.8 Critical — XSS, IDOR
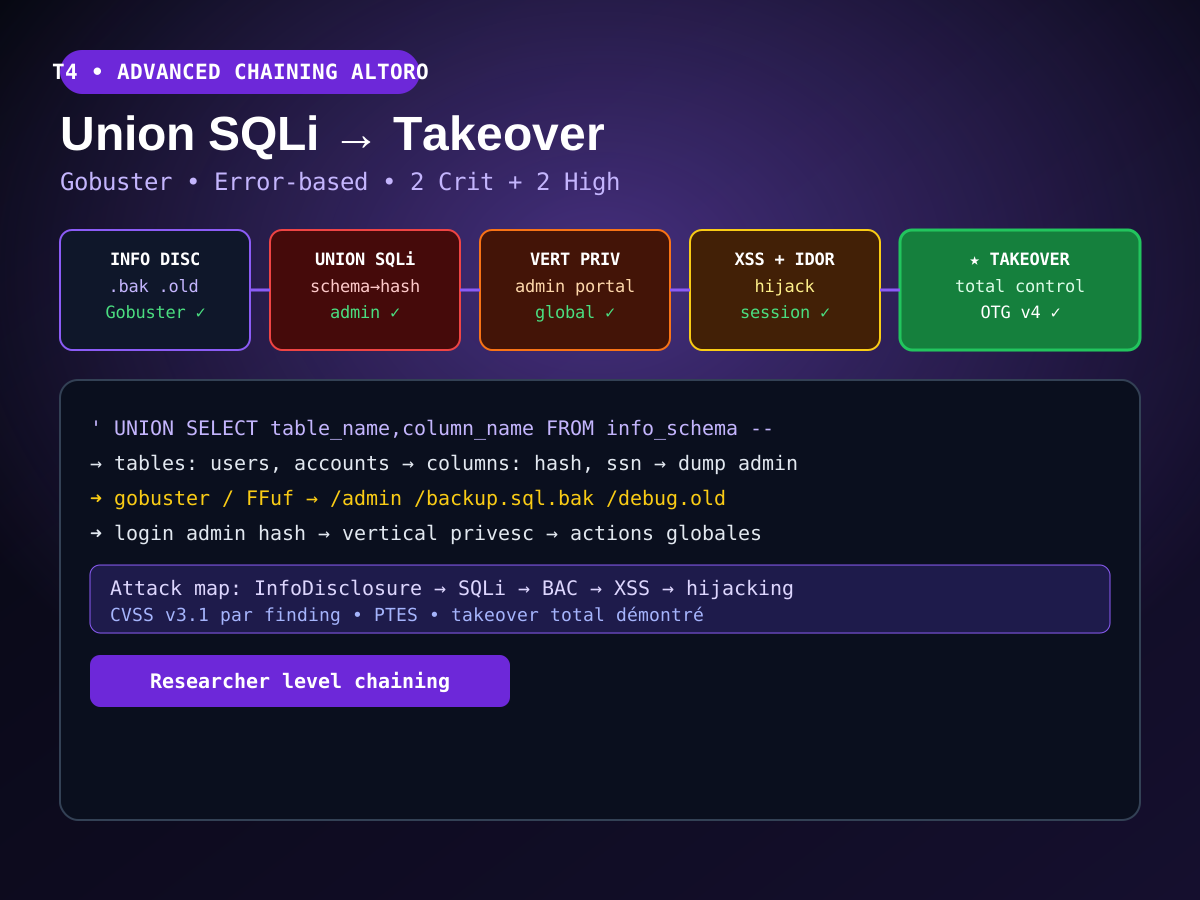
Union SQLi, fuzzing, takeover — CVSS
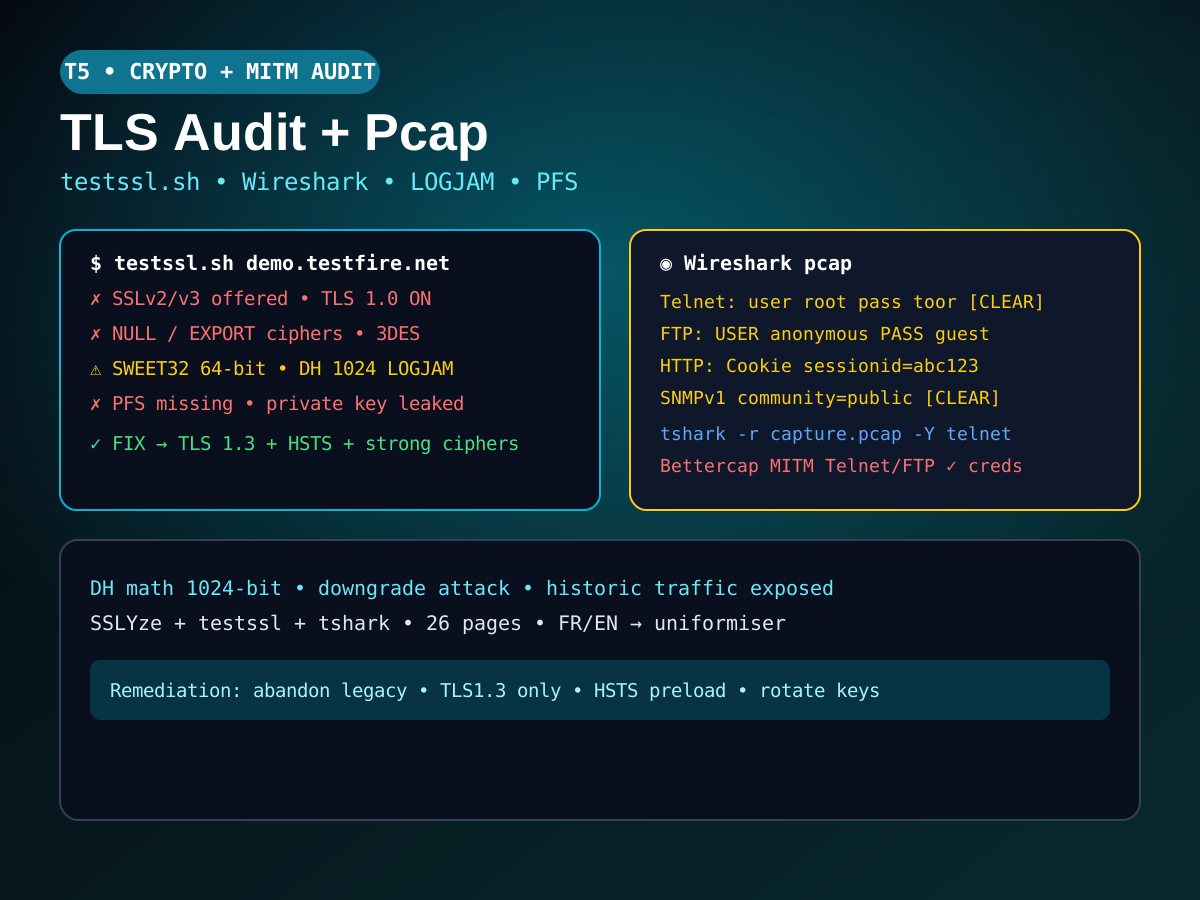
testssl.sh, Wireshark — TLS 1.3, LOGJAM
Structured kill chains, CVSS scoring and remediation — the way engagements should be documented.
Full kill chain from recon to root: how the Samba username map script yielded remote code execution, with CVSS scoring and remediation.
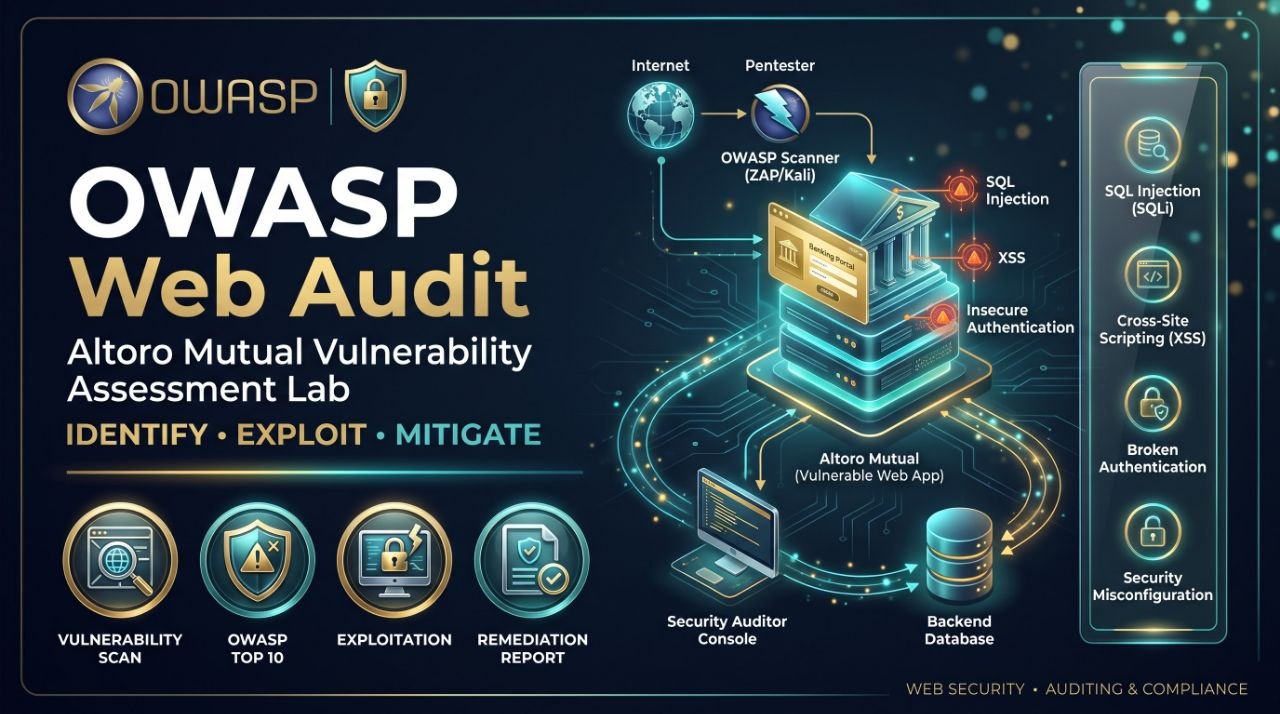
Altoro Mutual advanced exploitation: Union SQLi schema extraction, backup discovery, vertical privesc and session hijacking.
ARP spoofing with Bettercap, cleartext Telnet and FTP credential theft in Wireshark, LOGJAM and SWEET32 analysis, PFS hardening.
Youness ran a full pentest alone — reconnaissance, scanning, exploitation, post-exploitation through remediation — with professional reporting: an executive summary, CVSS tables and PoC screenshots.
Tasks 1–5 validated 4–5 out of 5 — PTES/OWASP methodology, command of Nmap, Burp and Wireshark, a documented kill chain, plus an AI detection project for SQLi and XSS deployed with Flask.
Open to internships, collaborations and anything security-related. The form opens your email app with everything filled in — no data is stored anywhere.